


Key Sorts And Operations In Key Management Service Nebius Ai Cloud
Key management, or encryption key administration, is the process of generating, exchanging, storing and managing cryptographic keys to make sure the security of encrypted knowledge. It is crucial for effective data encryption, as poor key management can lead to unauthorized access, information loss and information breaches. Key administration helps organizations keep encryption keys secure throughout their whole lifecycle, defending information integrity and minimizing the chance of unauthorized entry and data breaches.
Types Of Cryptography
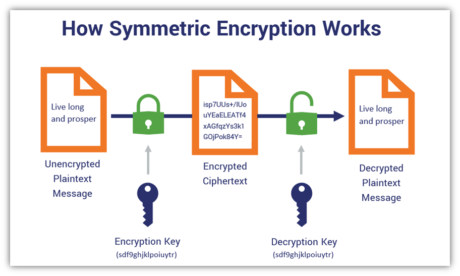
With the help of Steganography, we are able to cover any digital content just about like text, image, videotape, etc. Symmetric Key Cryptography is an encryption system where the sender and receiver of a message use a single frequent key to encrypt and decrypt messages. Basically, KMIP provides a common language for varied key management systems to speak and seamlessly operate together. Open-source instruments can benefit organizations that require excessive flexibility, need to keep away from vendor lock-in or should ensure clear safety practices. In DevOps, functions are constantly developed, examined and deployed, usually at a rapid tempo.

When Legacy Systems Meet Outsourcing: Bridging The Hole Between Business Expectations And Engineering Reality
For instance, if you wish to send a secret message to a pal, you each agree on a secret code (the symmetric key). You use this code to lock the message, and your friend makes use of the same code to unlock it. Cryptographic keys are analogous to the number mixtures used to safe a bodily protected. Only the approved user(s) of the secure have information of the safe mixture keys. CSPs are also responsible for creating the keys, destroying them, and using them to perform a selection of cryptographic operations. Cryptographic keys shall be generated within cryptographic module with at least a FIPS or compliance.
They additionally verify identities and ensure knowledge integrity through digital signatures. A cryptographic secret is a string of data used in encryption algorithms to safe data. It is essential for making certain confidentiality, integrity, and authenticity in digital communication.
It’s made to protect your prized possessions, however it could only achieve this should you adequately defend the important thing. For example, leaving the necessary thing under your doormat defeats the protection your lock supplies. Trade analysts now suggest cryptographic posture administration as a finest follow, signaling that the market has matured to the purpose the place steady cryptographic assessment is expected, not optional.
Symmetric algorithms are the most typical sort of encryption algorithm. They are known as symmetric because they use the same key for each encryption and decryption. Session keys are sometimes modified, normally utilizing a special session key for each message encrypted. Determine the cryptographic and key administration necessities on your utility and map all parts that course of or store cryptographic key materials.
Key Revocation And Destruction
The transition to post-quantum cryptography requires planning right now, even earlier than quantum computer systems are operationally viable. Organizations can’t put together for the quantum transition without first figuring out what cryptographic assets they have and where those assets are deployed. The discovery and inventory https://www.yokan.info/the-5-rules-of-and-how-learn-more-3/ practices described earlier in this guide turn into even more critical within the context of PQC migration. Completing the cryptographic stock image is crucial both for today’s preparedness towards present attacks, and for the future transition to quantum-safe algorithms. Cryptographic posture management is the practice of continuously assessing and enhancing an organization’s general cryptographic readiness. It connects discovery, policy, and lifecycle management into a steady improvement loop.
- You can schedule a key rotation to run at a convenient time, then cancel it if not finished when system resources are wanted again.
- European laws, including the CSA, more and more require organizations to reveal their cryptographic posture.
- It is the inspiration on which the safety of each encrypted asset depends.
- Automation is the enabler that makes every other key administration greatest apply sustainable at scale.
This follows the principle of securing knowledge at relaxation and is beneficial for reconstructing a key from archived keying data. FIPS186 specifies algorithms which are permitted for the computation of digital signatures. Message Authentication Codes (MACs) present knowledge authentication and integrity. A MAC is a cryptographic checksum on the info that’s used in order to provide assurance that the data has not modified and that the MAC was computed by the expected entity.
Cryptography is the science of defending info utilizing mathematical methods to make sure confidentiality, integrity, and authentication. It transforms readable information into unreadable type, stopping unauthorized entry and tampering. Defend information everywhere—enforce sturdy encryption, handle keys and secure sensitive information across on-premises and cloud environments. CloudHSM providers can extend these capabilities to the cloud, providing the same stage of security for cloud-based environments. Organizations that need to meet strict compliance necessities, such as PCI DSS or GDPR, might select HSM, understanding that keys by no means go away the safe environment.